Efficient and Comprehensive Risk Analysis
Find and fix Segregation of Duties and critical access risks across SAP and your other ERPs. The template ruleset has 1,150+ checks, and you can read and change every one of them.
Segregation of Duties Conflict Detection
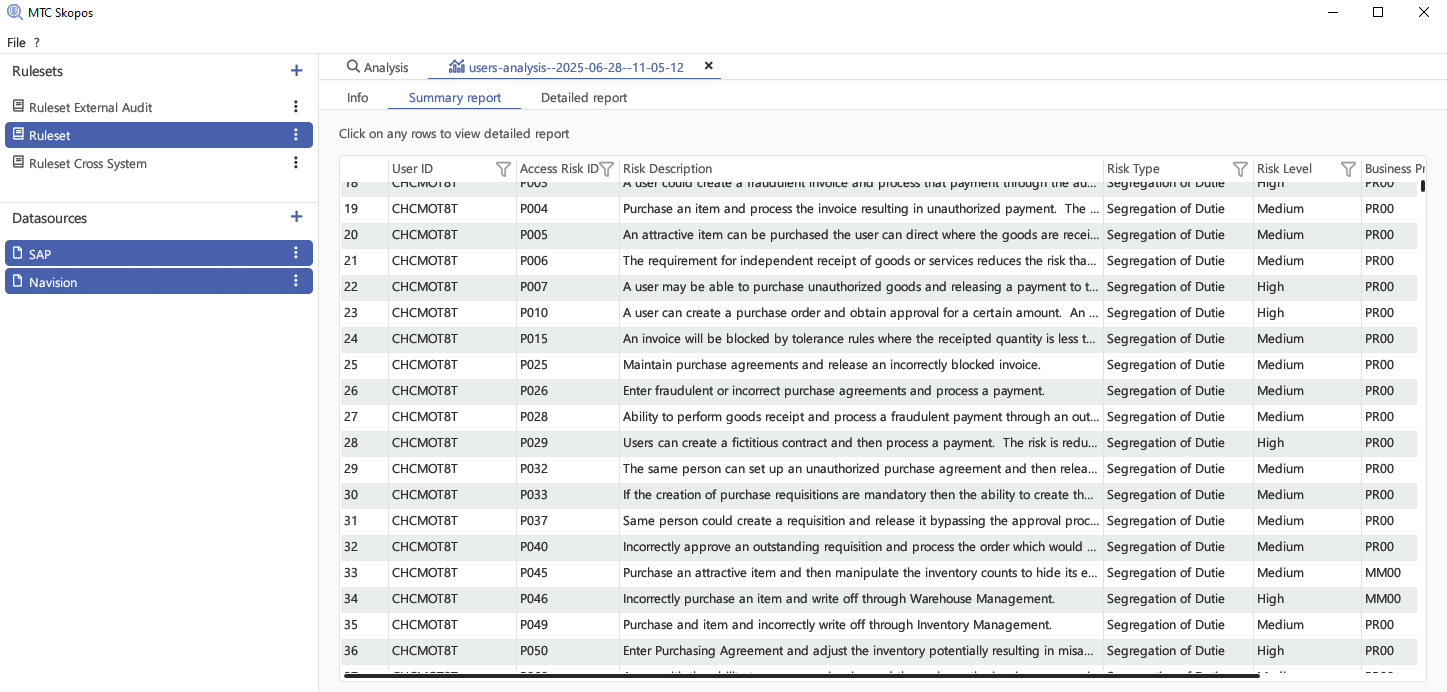
MTC Skopos detects SoD conflicts in SAP and any ERP, and applies organizational scope before it reports one: a user who creates vendors in company code 1000 and pays them in 2000 is not flagged. Derived roles and validity dates are resolved as well, so an expired assignment or an out-of-scope derivation never turns into a finding. You spend less time dismissing false positives, and the findings left are real ones. Why the depth of analysis changes the result
Template Ruleset Included
MTC Skopos ships with 350+ SoD risks, 700+ critical access checks and 100+ authorization quality checks (organizational values, maintenance activities in display roles). That is 1,150+ checks on the first run.
Treat it as a template. Review it and tune it to your own processes before you rely on the results. It also converts to SAP GRC format, so if you move to GRC later, your ruleset goes with you. Ruleset maintenance
Permission Simulation
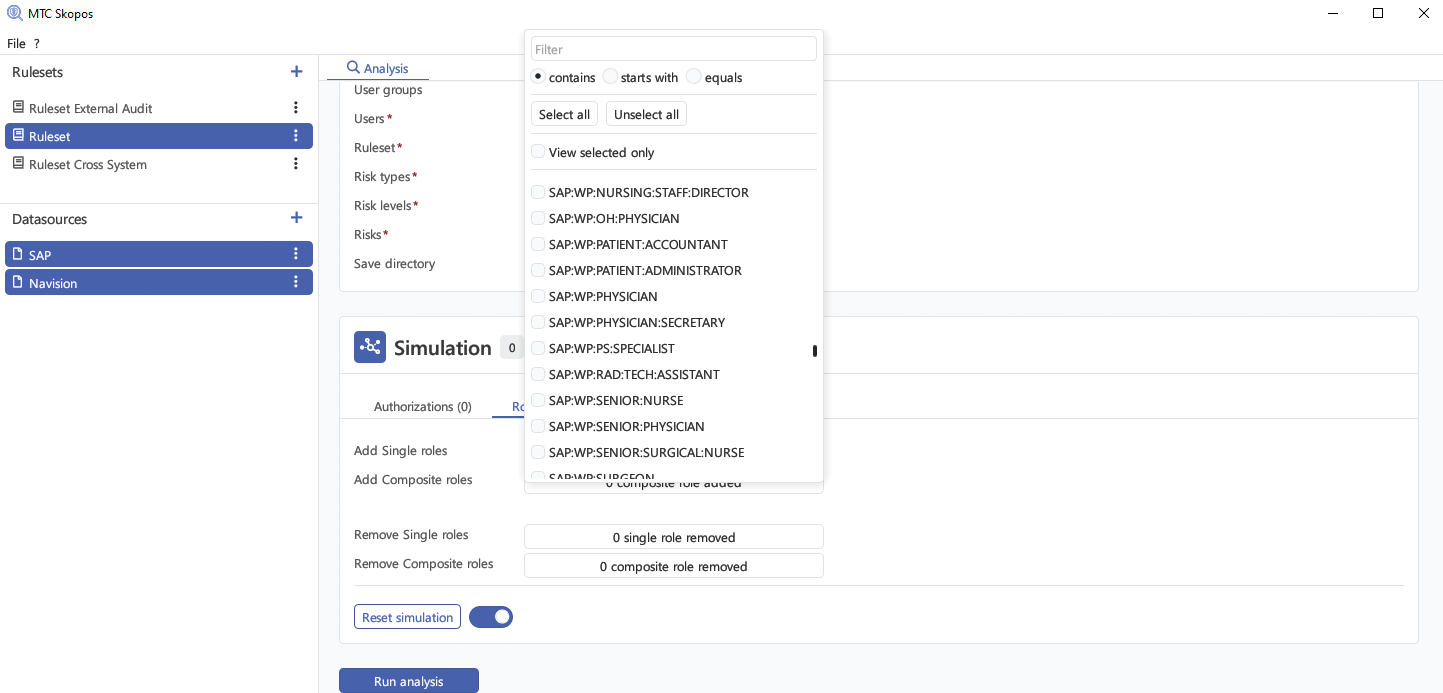
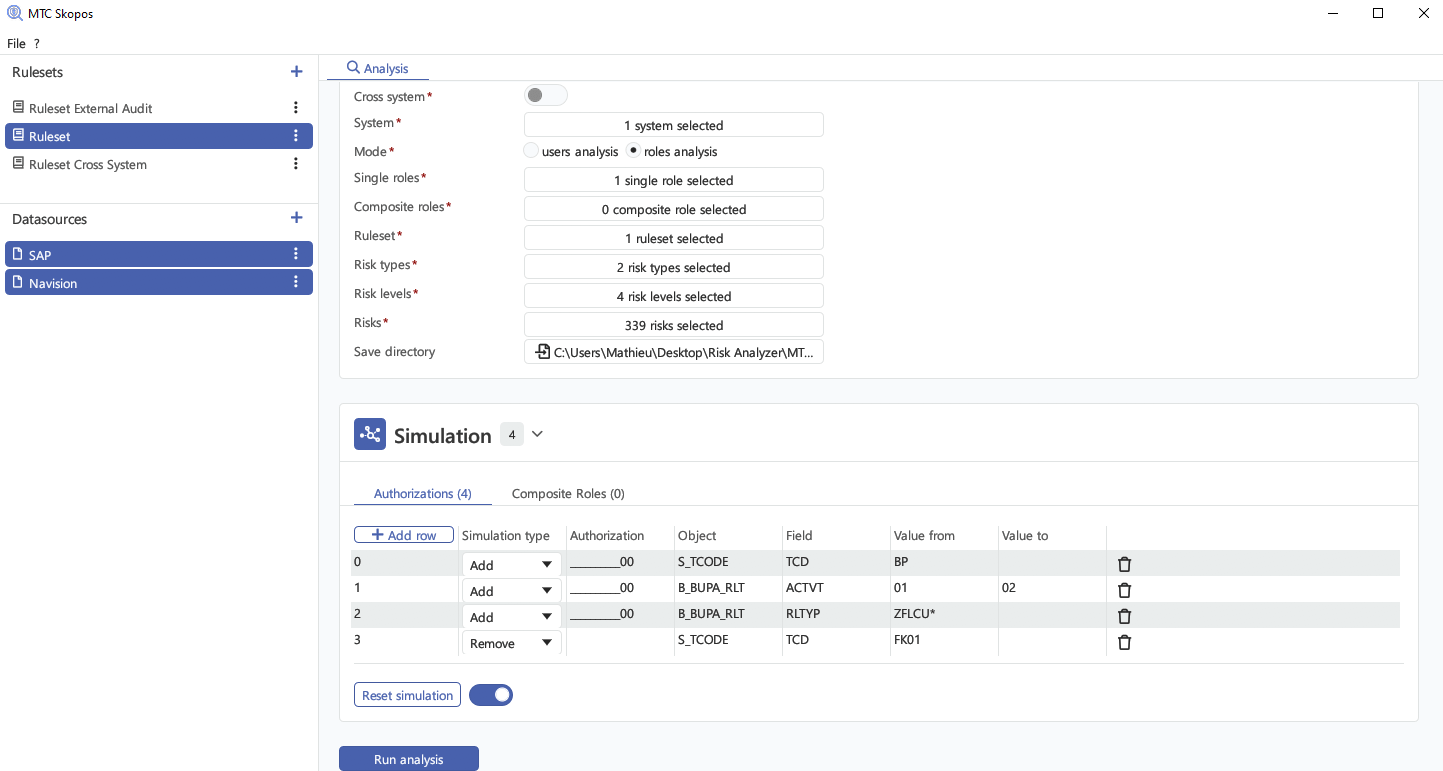
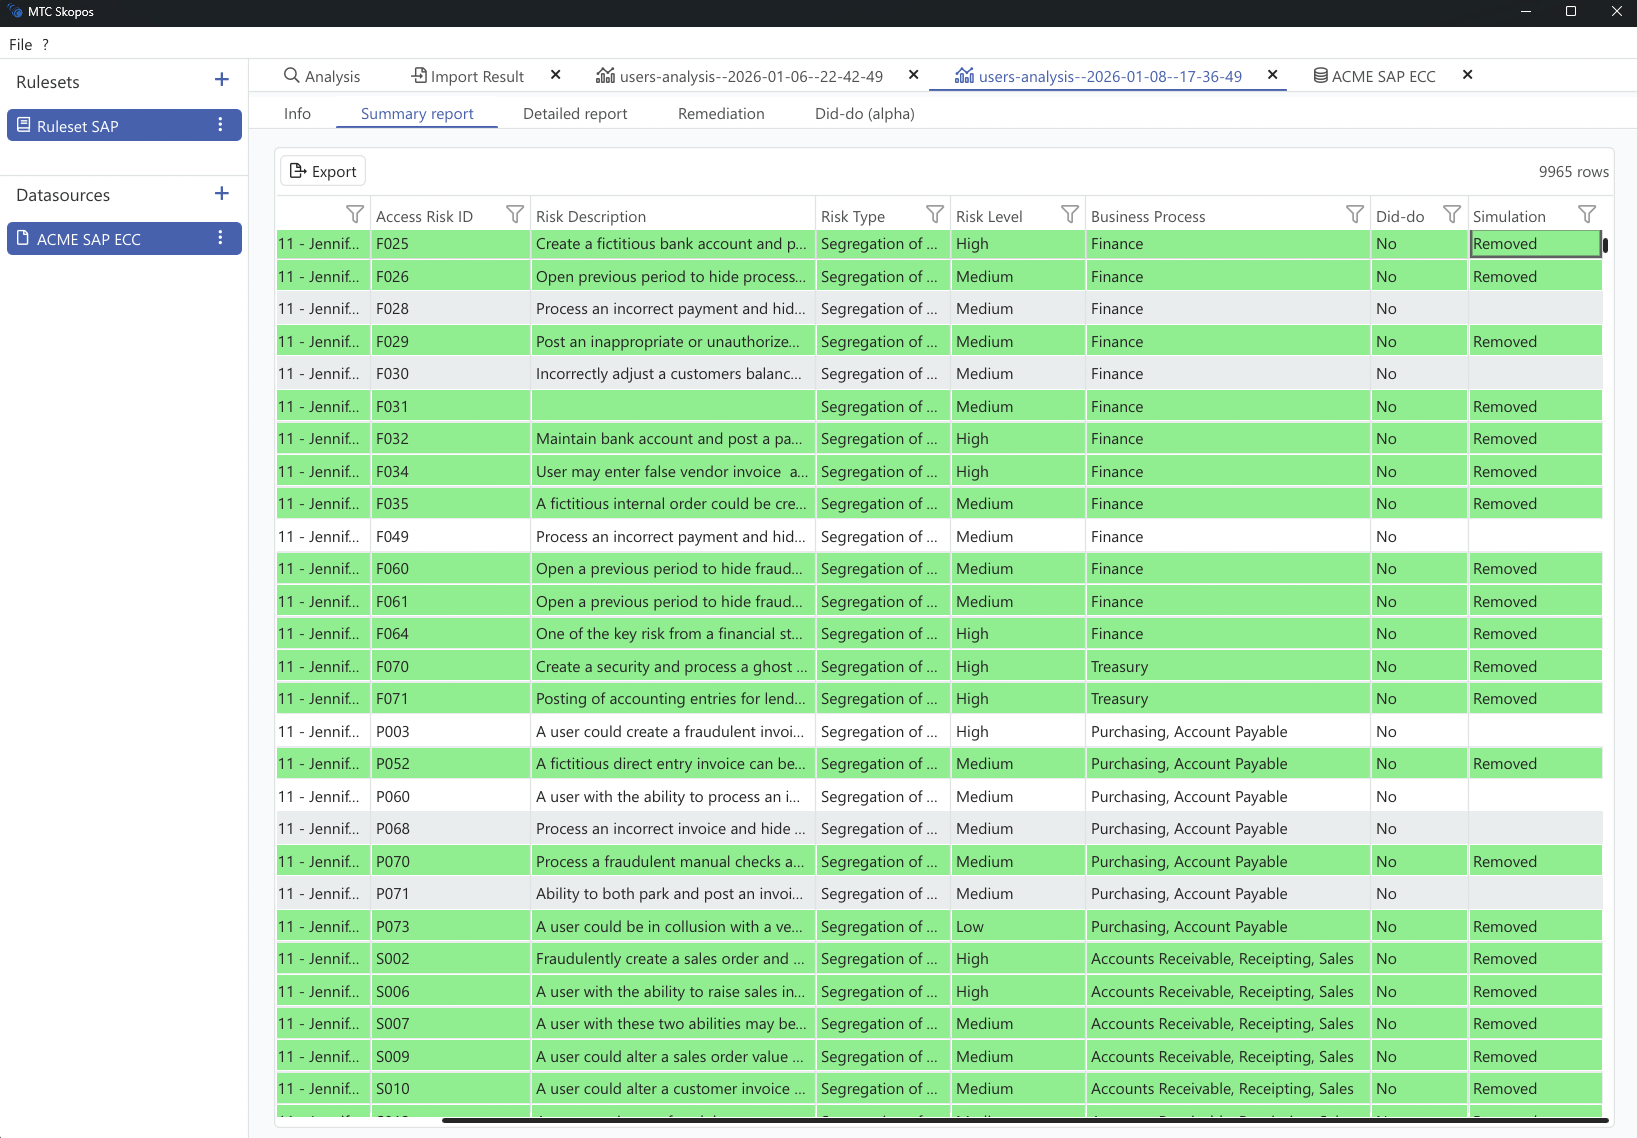
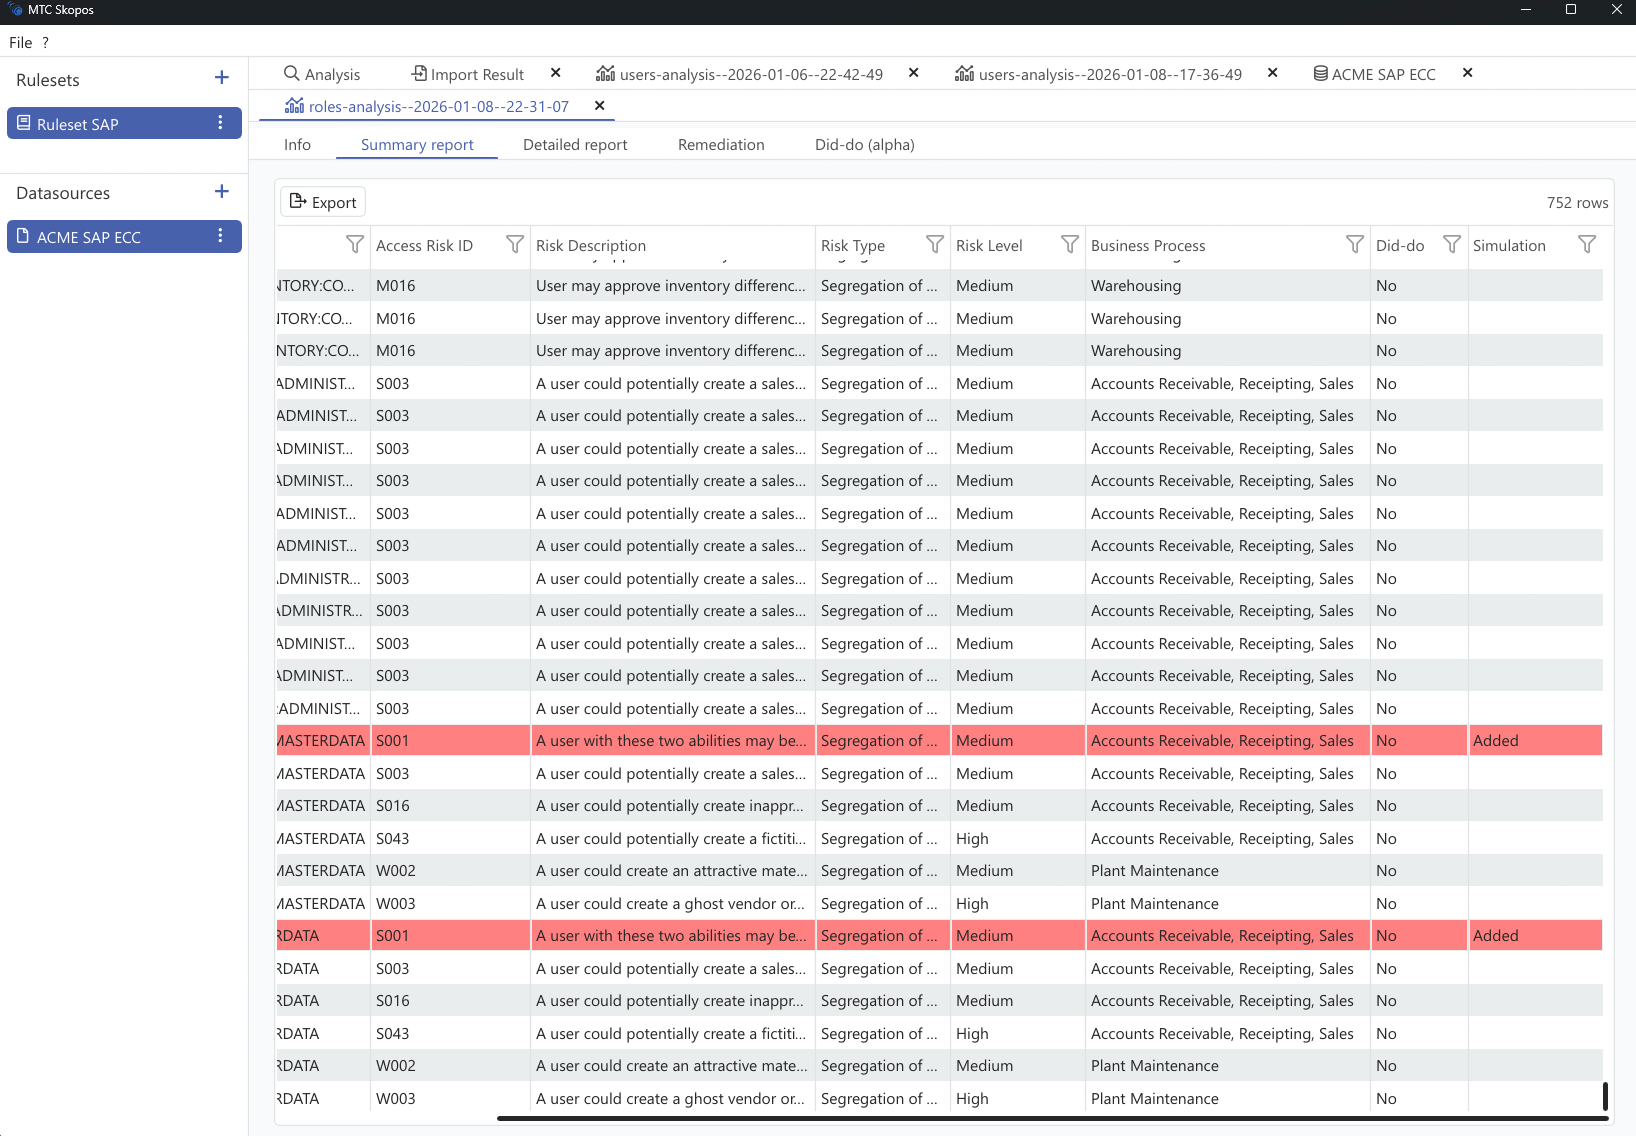
Test role and authorization changes before applying them to production using simulation
feature.
See exactly how changes will impact user access and identify potential access
risks.
Simulate with Confidence:
- Adding or removing user role assignments
- Adding or removing authorization within existing roles
- Creating new role
- Cross-system access combinations and their security implications
Preview, validate, then deploy - ensuring every access change enhances security rather than creating
vulnerabilities.
Advanced Remediation
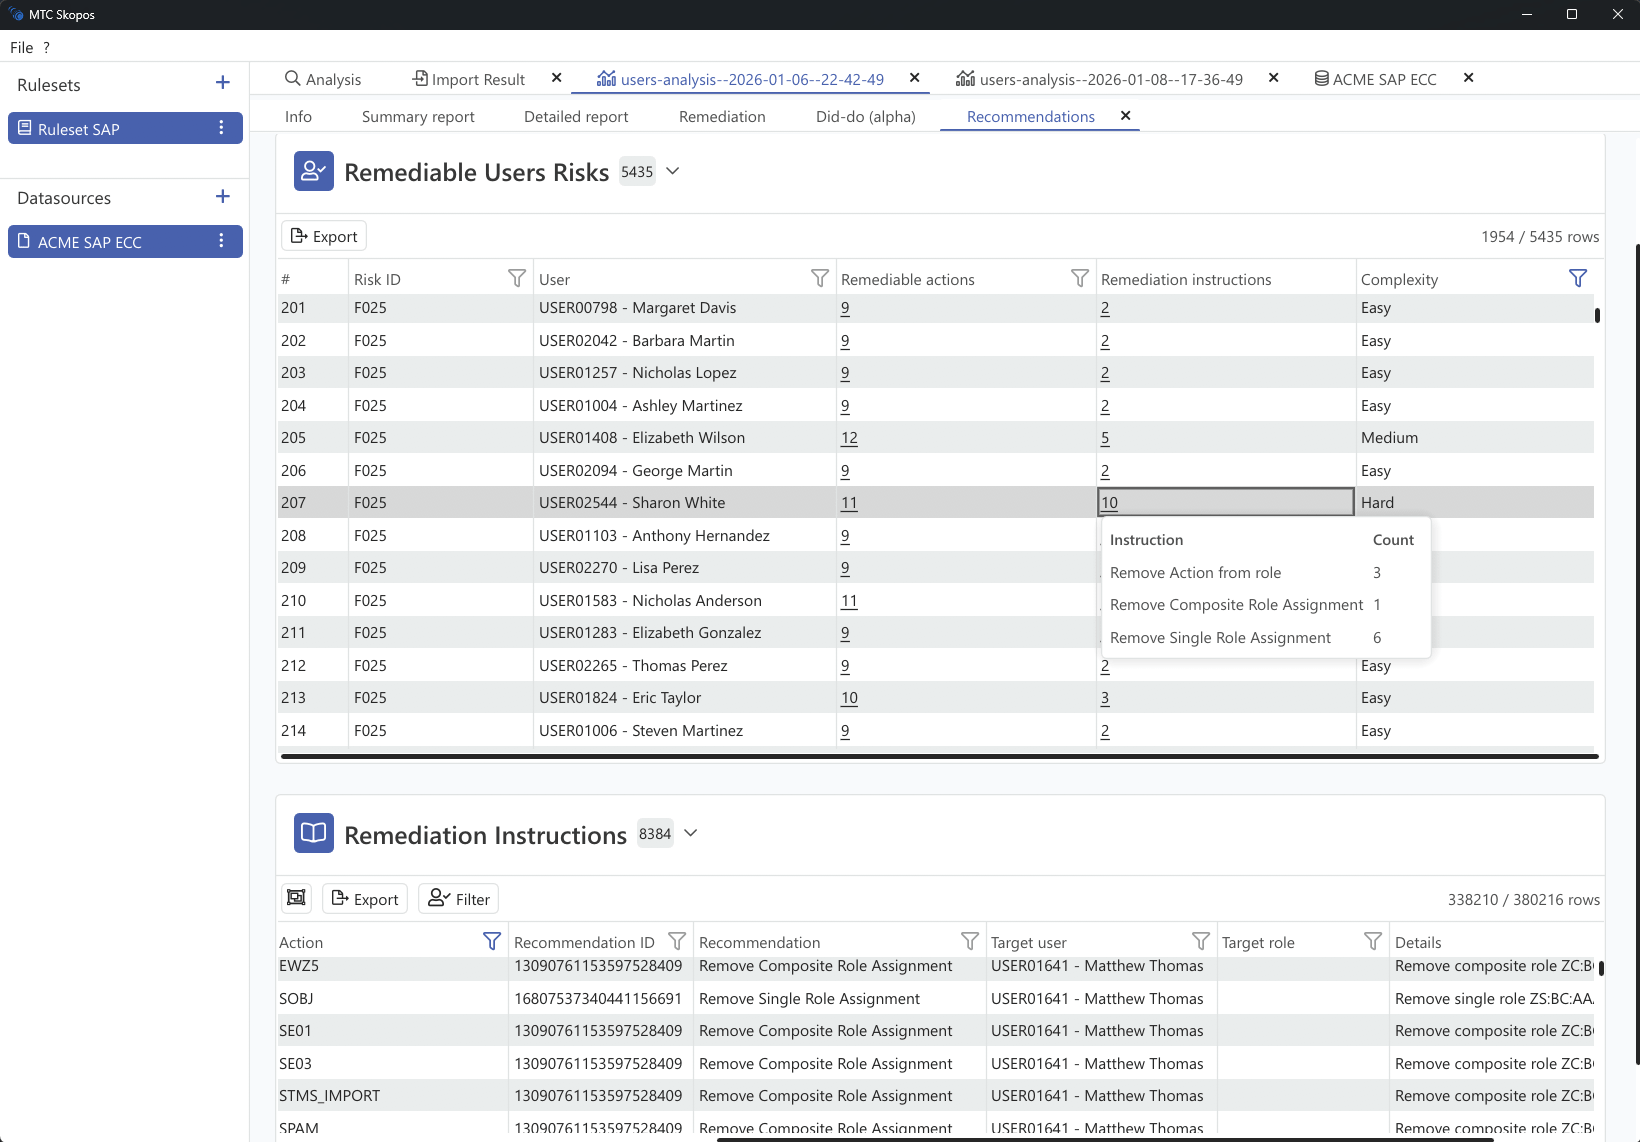
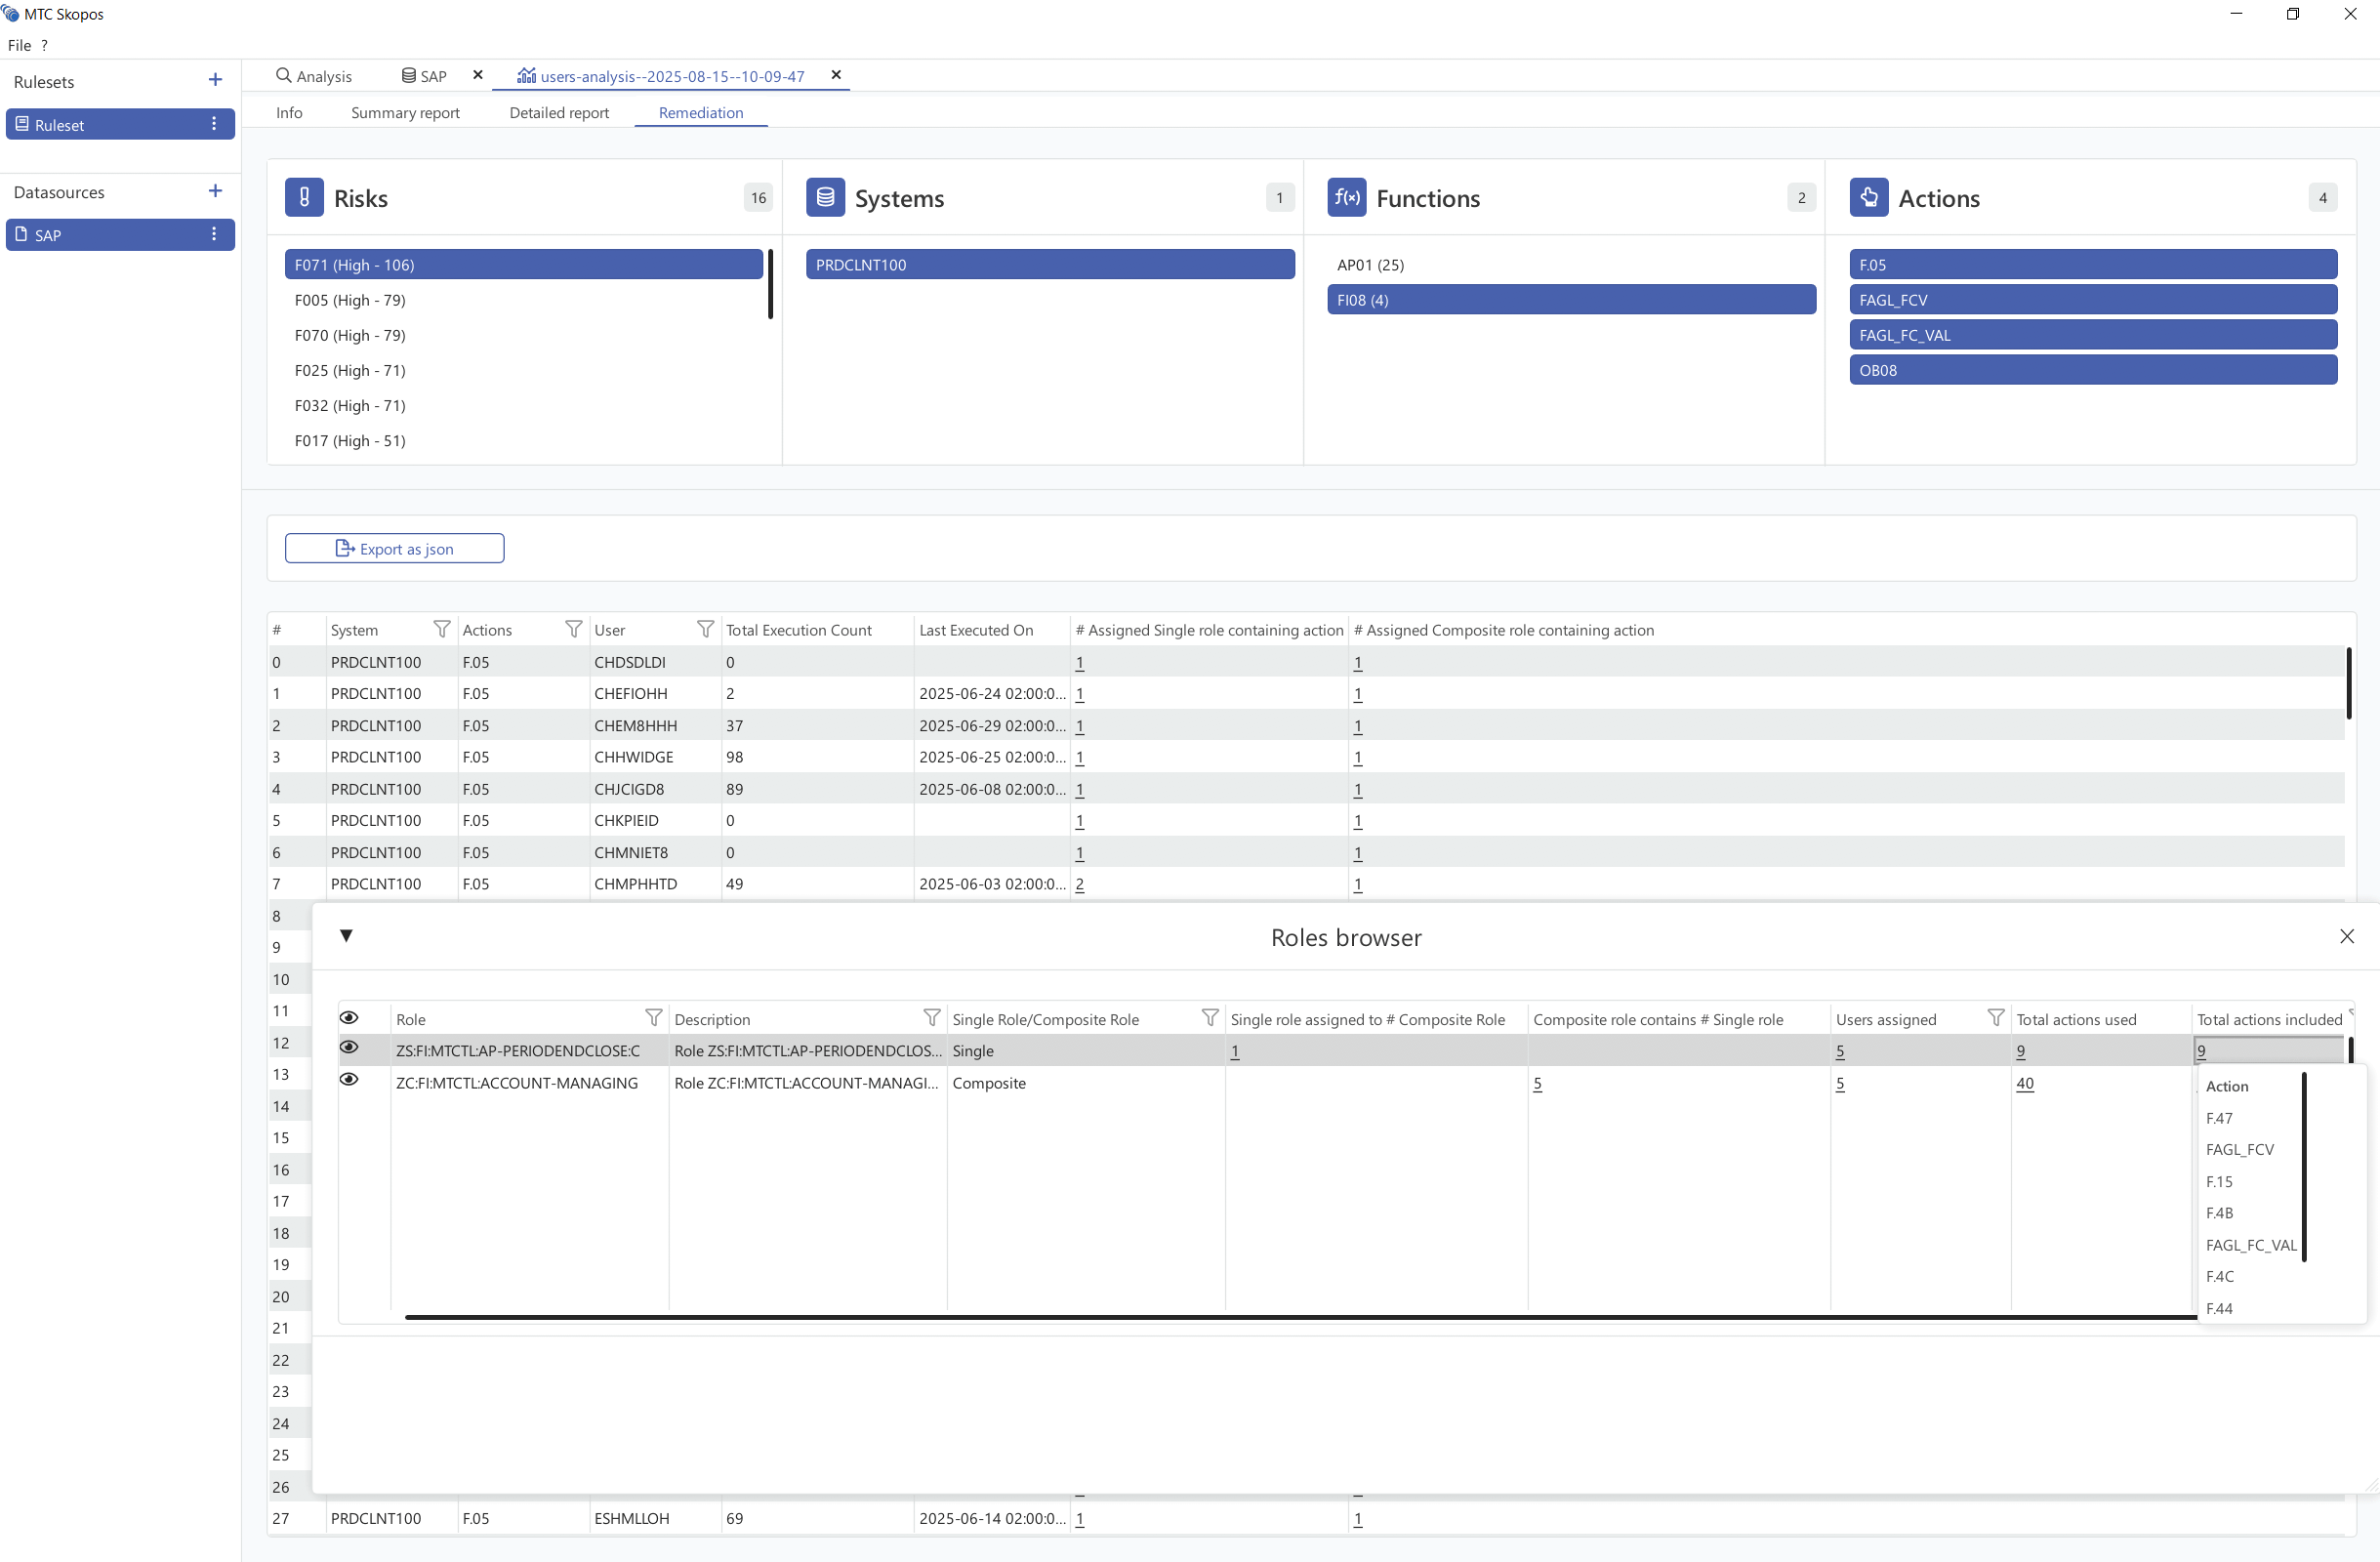
Finding a conflict is the easy part. For each one, MTC Skopos proposes a fix: which role assignment to remove or replace, and in what order, based on criteria you set. It looks at usage data first, so it can tell access nobody uses, which can go today, from access a process still depends on. How it works
Remediation Reports put that plan into a document for role owners and auditors to sign off. Learn about AI remediation
Did-Do Analysis
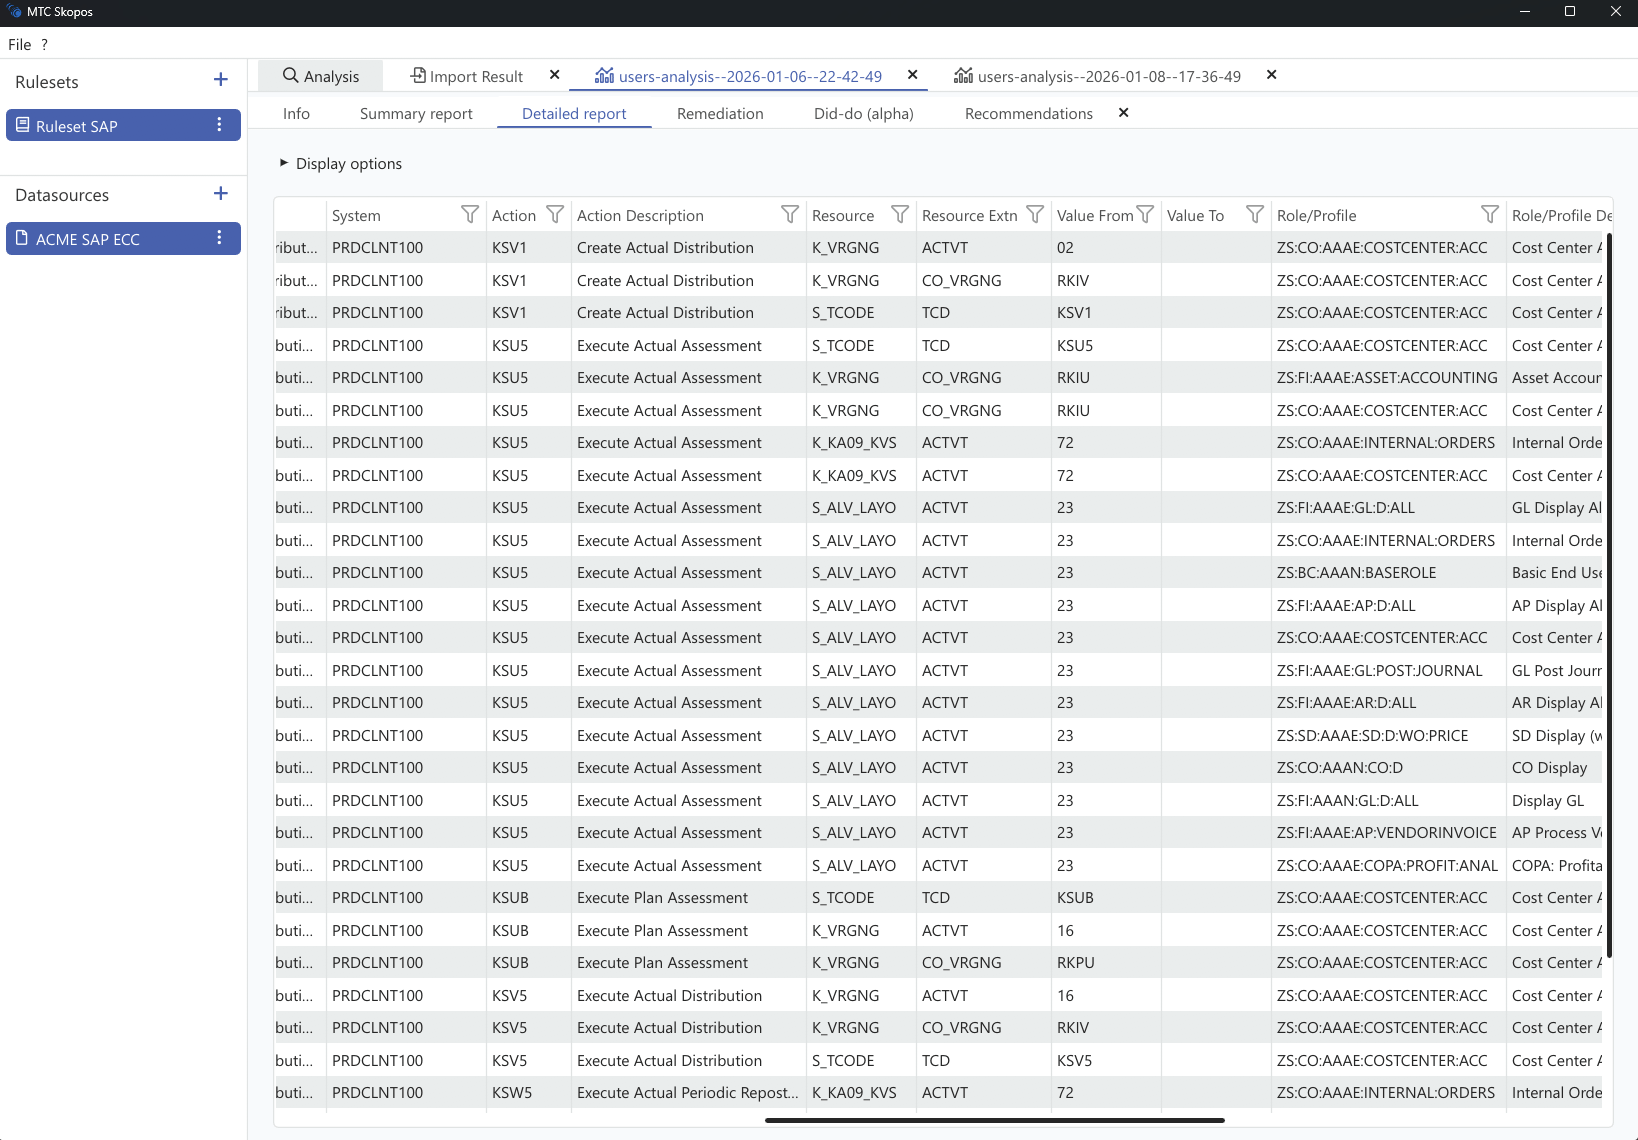
SAP GRC does can-do. We do did-do. Traditional tools show who could exploit a conflict. MTC Skopos shows who actually did by correlating access with change documents. Focus remediation on risks that materialized, not theoretical violations. See how it works
Cross-System Risk Detection
Assess risks arising from access across multiple systems, and identify critical
combinations that
span different platforms.
IAM Business Role Analysis
Your IAM assigns the access. We analyze the risk. Import business roles from Microsoft Entra, SailPoint, or ServiceNow and detect SoD conflicts in the access they grant, across every connected system. Every risk shows the business role behind it, and you can simulate bundle changes before touching the IAM. Analysis only. See how it works
Ground Truth for Your AI
Give a model a raw authorization export and it will answer with confidence. It won't know that a role grants a transaction without the authorization object behind it, or that an assignment expired last quarter. MTC Skopos sorts that out first: composite and derived roles are expanded, validity dates and organizational scope are applied, and only then does a model see the data.
You pick the model. Claude, ChatGPT or any stdio-compatible client can query the results through the MCP server. The built-in assistant works with any OpenAI-compatible API on your own key. With a local LLM, nothing leaves your network. User, role and system names are anonymized before they reach any model. Explore AI integration
SAP Role Designer (AI)
Describe your requirements to our AI and automatically generate optimal role designs with default authorization configurations.
Data Sovereignty
Your SAP authorization data stays on your network.
MTC Skopos is a desktop application with no cloud component. Nothing is sent to MTC or stored by a third party. The data stays on your machines under your own security policies, which a SaaS GRC tool can't offer.
*SAP RFC connection may traverse your network; all analysis runs locally.
Also Included
The rest of what you'd expect from an SoD tool:
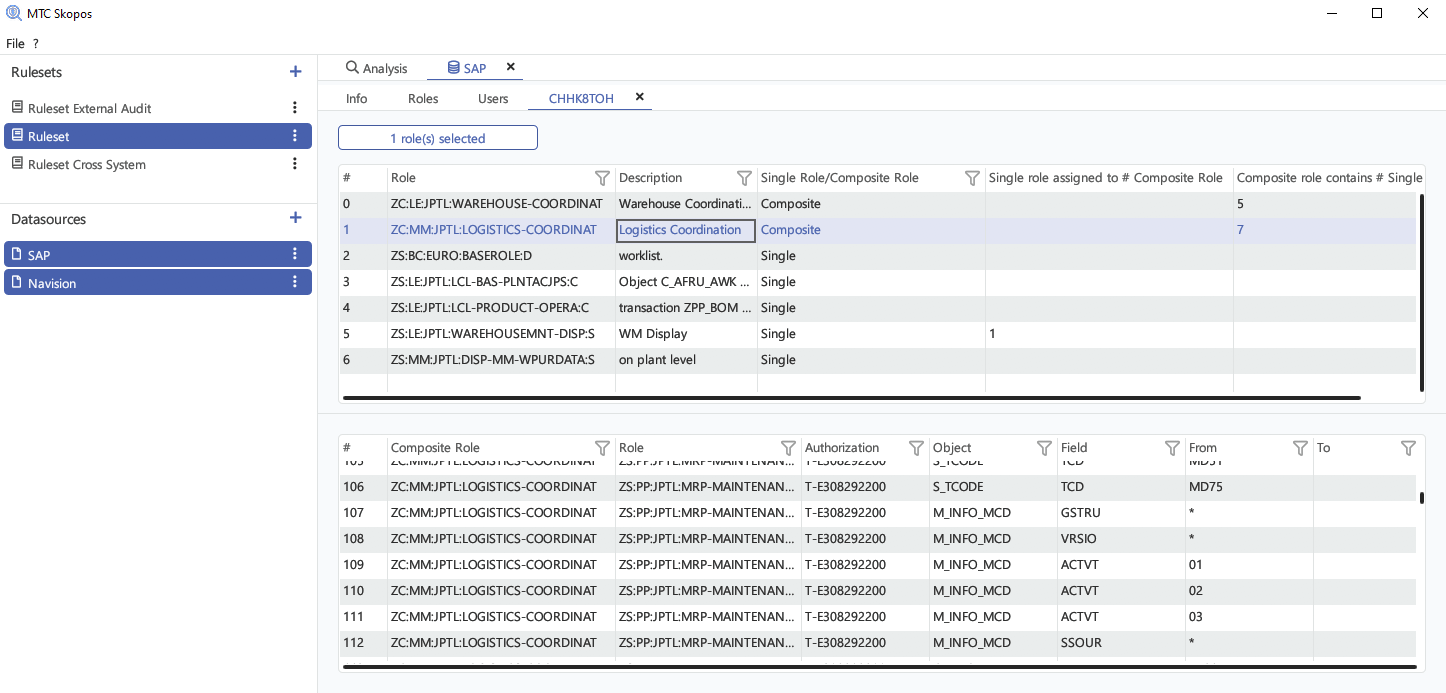
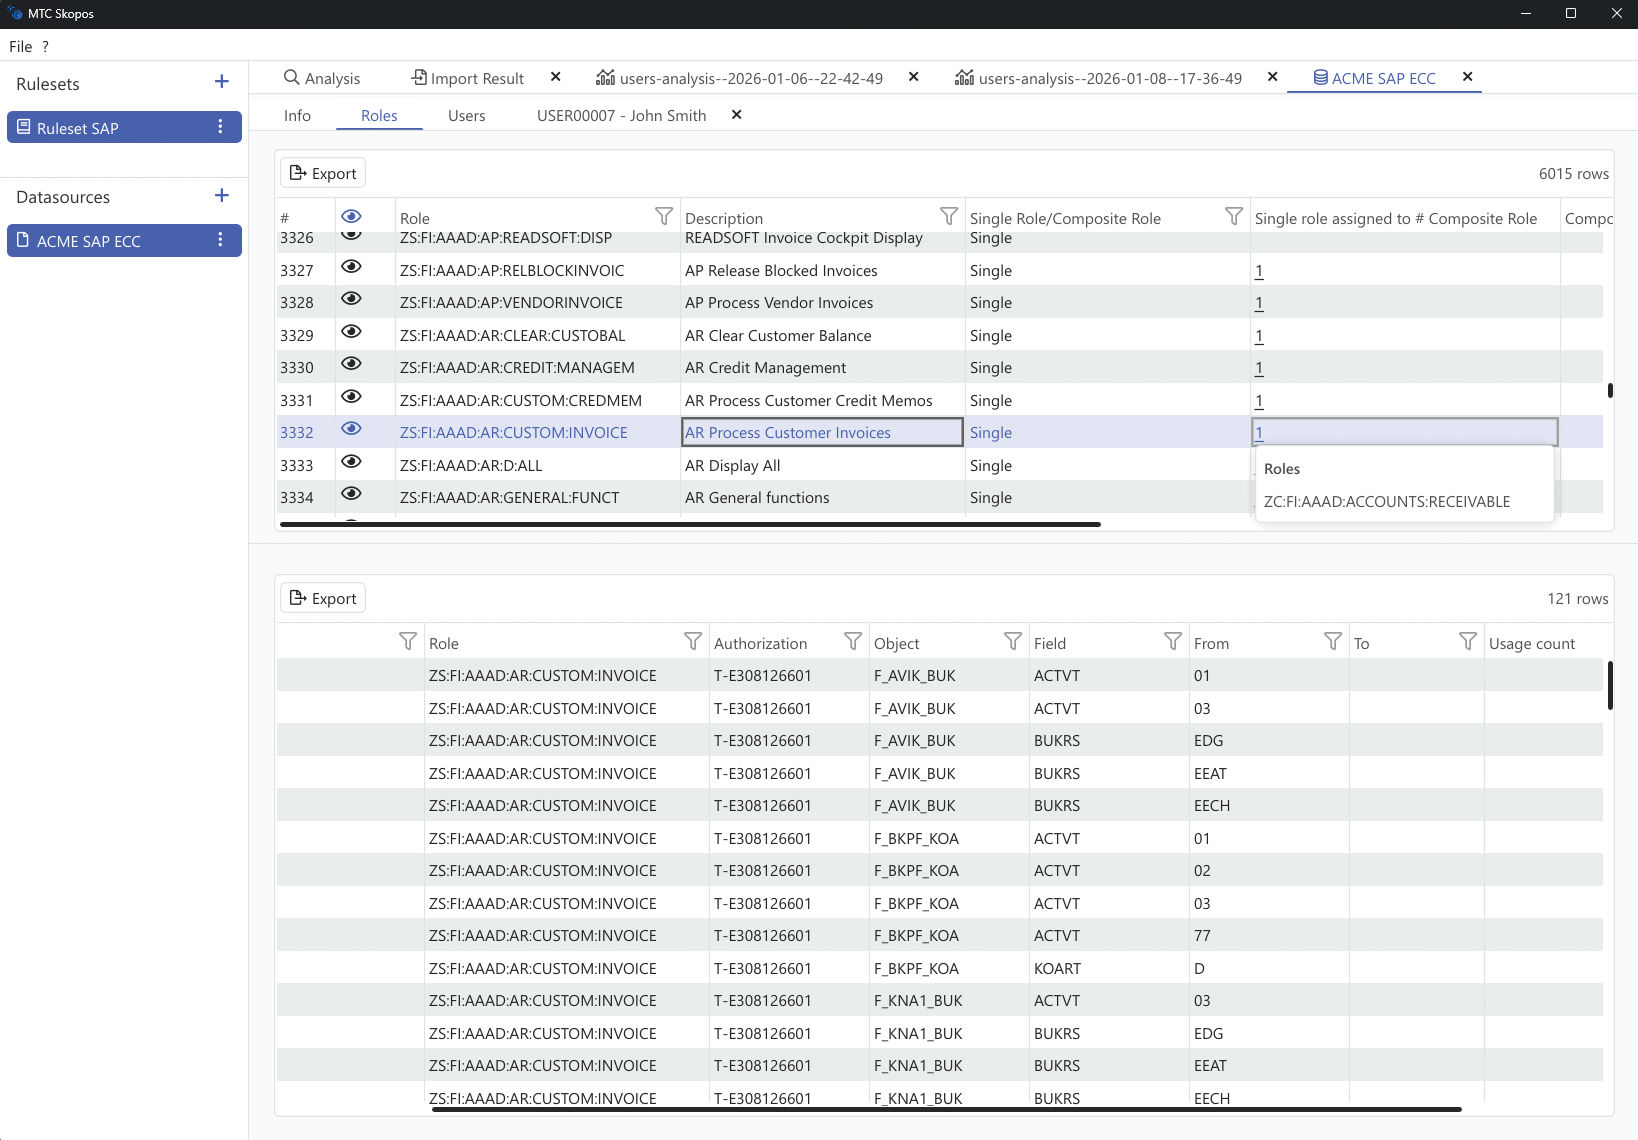
- Users and roles analysis, by role or by user, including overprovisioning and the FUE licence impact of each user and role
- User & Role Explorer for browsing your authorization concept. It stays fast on large systems
- Executive reporting: each analysis opens on a dashboard of conflicts by risk level and business process, the most frequent risks and the users with the most conflicts. Click a risk to see the actions behind it. A Microsoft Power BI report (.pbix) is included. See reporting capabilities
- JSON and CSV exports that load directly into Power BI, Tableau, Python or R, compact enough to keep AI token costs low
- Speed: a single-user check in under a second, a full 10,000-user system in under two minutes on a standard laptop. Why we built this








 Minutes (portable app)
 3-6 months implementation


 Ask ChatGPT
 Ask Claude
 Ask Perplexity
 Ask for a demo